
Alerts and forwarded events now show what changed, not only that something changed. Plus several security fixes.
Alerts show what changed
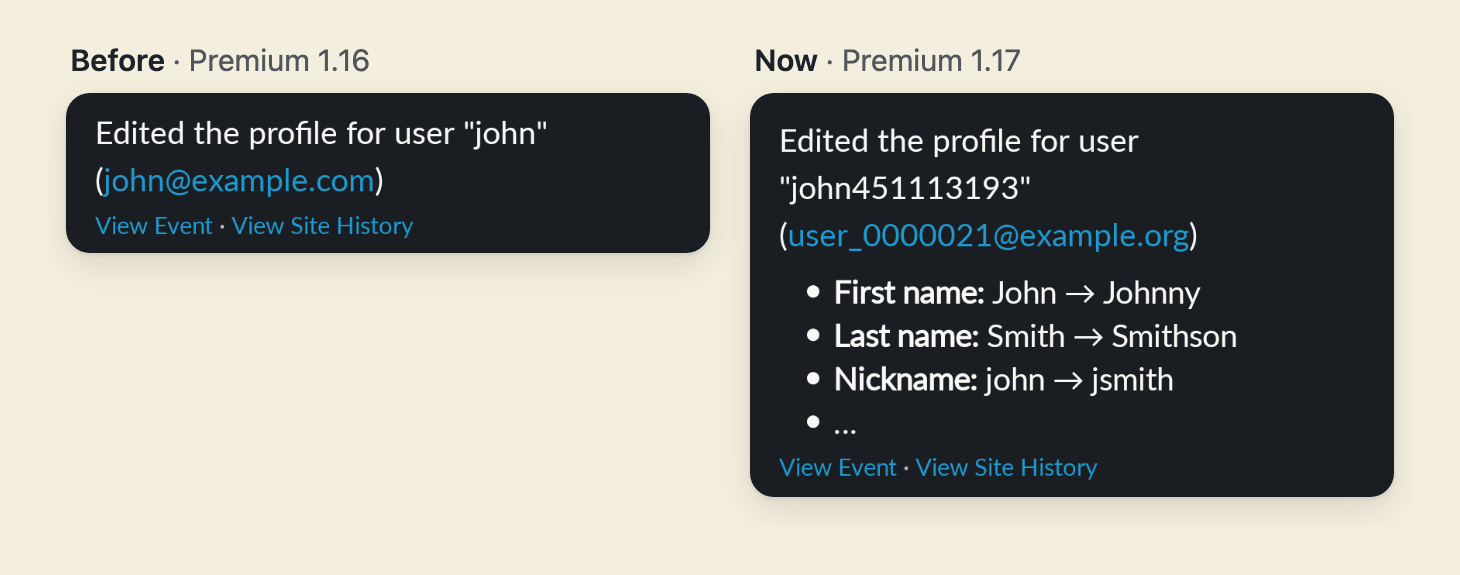
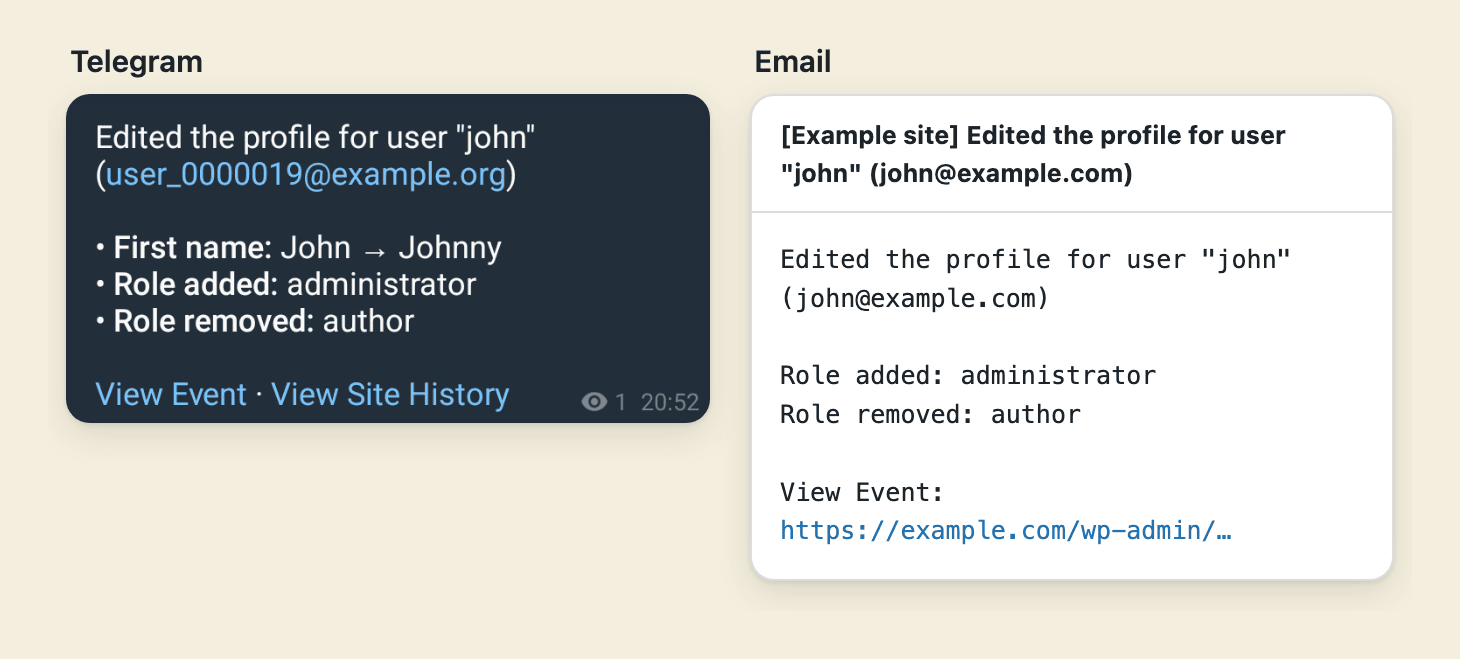
An alert used to say “Edited the profile for user john”, and you had to open the log to see what was edited. Now the alert lists it: the roles added and removed, the old and new name. Slack and Telegram get a bulleted list, Discord and email up to three lines.
Forwarded events (log files, syslog, Splunk, Datadog) include the same details when you run Simple History 5.36.0 or later. Webhooks get two new placeholders for them, {details} and {details_json}.
Update from Dashboard → Updates. If something looks off, let me know.
Full changelog
Added
{details}and{details_json}placeholders for the webhook body, with what changed in the event.
Changed
- Alerts show what changed, like the roles added to a user: a bulleted list in Slack and Telegram, up to three lines in Discord and email.
- IP addresses with the last part removed are now called masked instead of anonymized, since they can still be linked to a person.
- The “Read full release notes” link in update details has tracking parameters, so we can see if the link gets used.
Fixed
- The setting for logging failed logins of existing users also covers wrong two-factor codes.
- Forwarded events (JSON Lines, logfmt, syslog, Splunk, Datadog) include what changed, like the roles added and removed in a profile edit, with Simple History 5.36.0 or later.
- Log forwarding and alerts work with any port, like the 8088 that Splunk uses, and with servers on your own network.
- Log forwarding records connection errors and switches off a channel that keeps failing, also for events that happen in wp-admin.
Security
- Event text in Discord and Slack alerts could show as clickable links or mention everyone. It is now escaped, and alerts never ping anyone.
- A destination name or a webhook’s response could run as HTML in the alert destination Test result.
- On multisite, only network administrators can configure the Remote Syslog and External Database channels, so subsite administrators can no longer use them to probe the internal network.
- The JSON feed now refuses an empty secret and respects the setting that hides the RSS feed.
- Line breaks and terminal control characters in event text could start forged lines in logfmt and local syslog output.
- The block editor activity panel and the table view now respect Stealth Mode, with Simple History 5.36.0 or later.